Share on social
Apr 4, 2025
Lorem ipsum
[BlackLock & DragonForce]
In this blog series we spotlight one of the stories from our cybersecurity newsletter, Beacon.
Last week threat hunters successfully infiltrated the online infrastructure associated with BlackLock ransomware, uncovering crucial information about their modus operandi as a result.
According to Resecurity, identification of a vulnerability on the leak site of the group made it possible to extract configuration files, credentials, and a history of executed commands. This also resulted in clear web IP addresses being revealed, which were hidden behind Tor infrastructure.
BlackLock, which emerged in January 2025 and was previously known as El_Dorado, had listed 46 victims prior to the incident. Coincidently (or maybe using the same exploit) BlackLock’s leak site was also defaced by another ransomware operation known as DragonForce, who leaked chat logs that appear to show BlackLock's communications with its victims, among other files.
At the time of writing, DragonForce is making further waves in the cybercriminal community after alleging a merger with RansomHub, the most active ransomware group of 2024.
DragonForce made an announcement on the RAMP cybercrime forum stating that it had become partners with RansomHub and would merge their infrastructure. This announcement came after a brief period of uncertainty and speculation in the cybercriminal underground in regards to the reason that RansomHub’s data leak blog was inaccessible. At the time of writing, the blog is still offline.
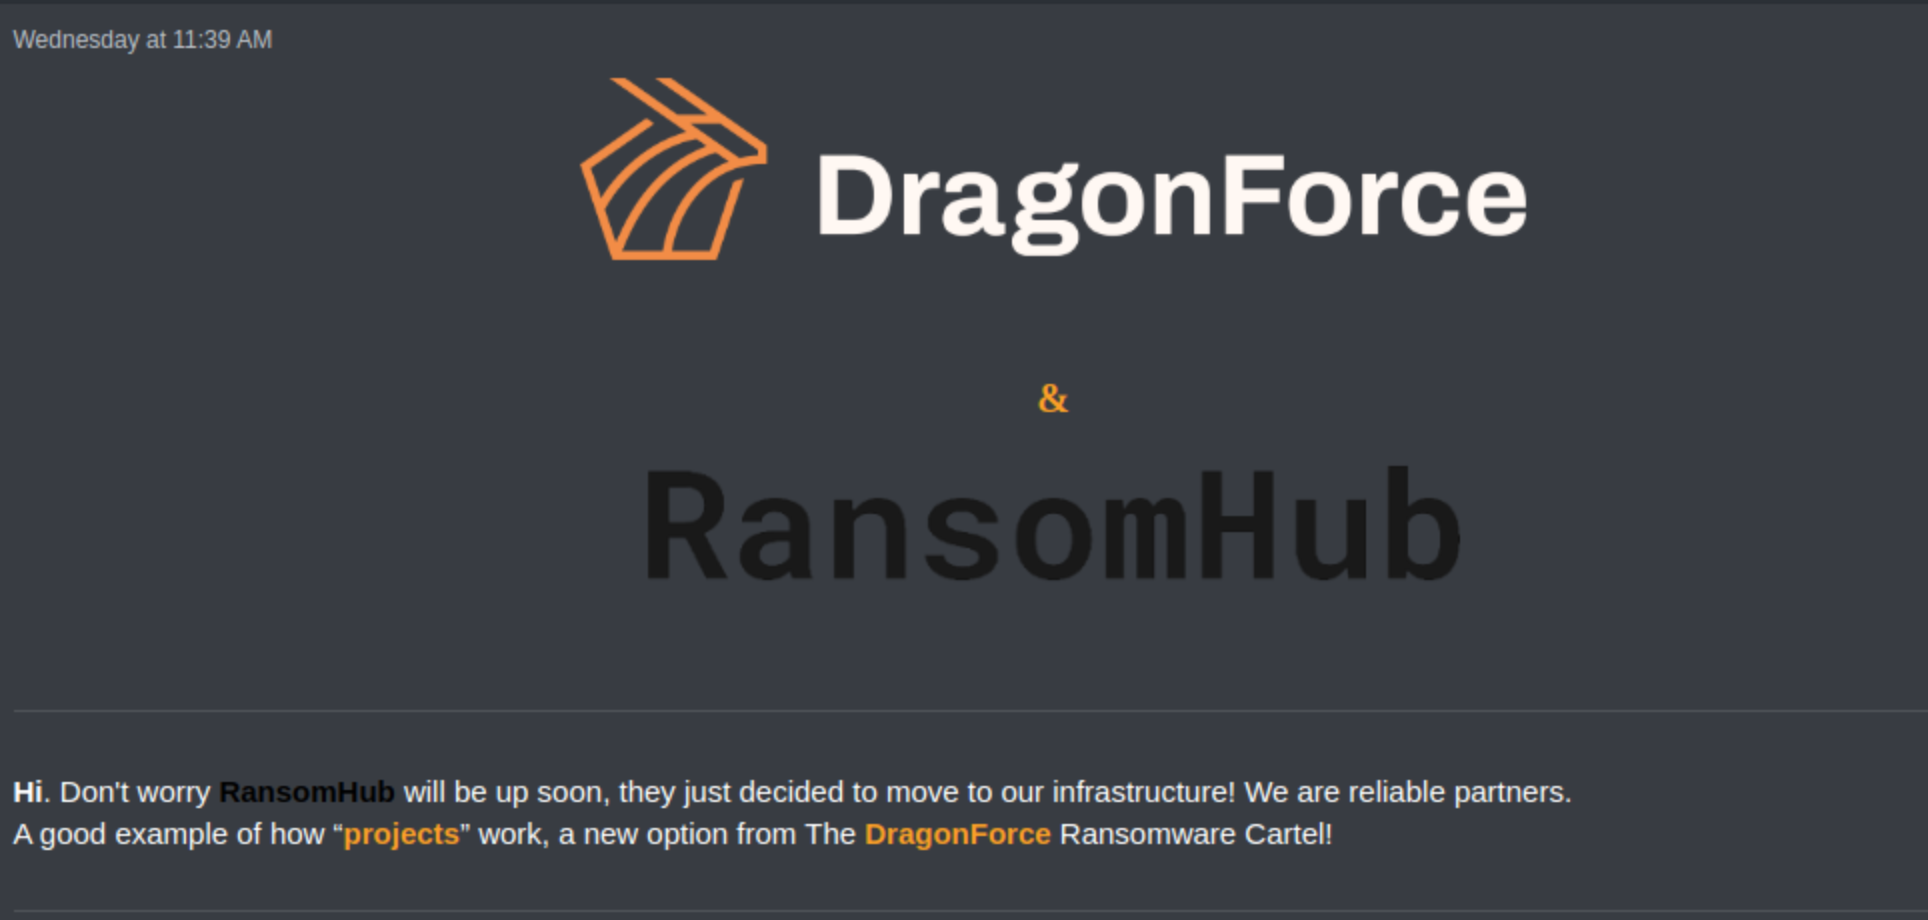
It remains unclear whether this claim is correct or whether this is another hostile action of DragonForce against a fellow ransomware group. The announcement was met with various reactions from multiple threat actors, some expressing concern or asking why the administrator of RansomHub, known as "koley", failed to disclose anything about the situation.
If you’d like the latest dark web news and insights delivered into your inbox every Thursday at 10am, SIGN UP to the email version of Beacon.